Frequently asked questions: Single Sign-on with SAML protocol
Nintex Workflow Configuration supports single sign-on (SSO) experience using Security Assertion Markup Language (SAML) 2.0 protocol. Read this guide to find out about this new capability and what it can provide for your tenant.
On this page, you'll find:
-
How does single sign-on using SAML work for Nintex CE Platform?
-
What are the three main entities involved in single sign-on?
-
What are the benefits of configuring SAML in Nintex CE Platform?
-
Do I need to bulk onboard users when single sign-on is configured?
-
What do I need to configure SAML for Nintex CE Platform using my preferred identity provider?
-
Security-related questions about SAML configuration in Nintex CE Platform
What is SAML?
Security Assertion Markup Language (SAML) is an open standard for exchanging identity authentication data between an identity provider An identity provider (IdP) stores and authenticates the identities of users to log in to system, files, or applications. and an application or service provider such as Nintex CE Platform.
What is single sign-on?
Single sign-on (SSO) is an identity authentication system that allows users to access multiple applications by using one set of credentials.
How does single sign-on using SAML work for Nintex CE Platform?
Nintex CE Platform uses SAML to support single sign-on. With SSO enabled, users can securely and conveniently sign in to Nintex CE Platform using the same set of credentials used in other applications such as Outlook or Office 365. Users are no longer required to create separate credentials to access Nintex CE Platform.
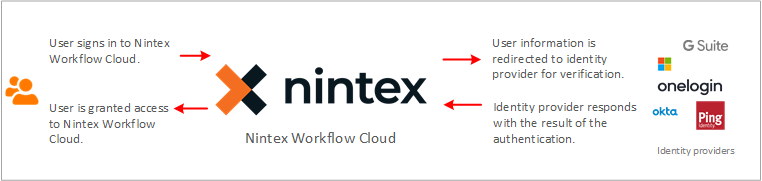
What are the three main entities involved in single sign-on?
- Application or service provider: The application or service provider we want to enable with single sign-on. In this case, our application or service provider is Nintex CE Platform.
- Identity Provider (IdP): An identity provider authenticates and manages the identities of users. Nintex CE Platform supports any identity provider that supports SAML including:
- Google Suite
- Okta
- OneLogin
- PingOne
- Active Directory Federation Services
- Azure Active Directory (can also be configured with SAML to enable SSO)
Note: For the steps to configure SAML in Nintex CE Platform with identity providers listed above, see How do I configure SAML in my Nintex CE Platform tenant?.
- A user: A person whose credentials are authenticated in the identity provider. The account credentials include an email address with a domain used in both the application and identity provider. For example, user@nintex.com.
What are the benefits of configuring SAML in Nintex CE Platform?
After you successfully set up single sign-on in Nintex CE Platform with your preferred identity provider using SAML, the following benefits apply:
- User experience: Users no longer need to create a separate username and password to access Nintex CE Platform. This saves time and the need to remember an additional set of login credentials.
- Increased security: Administrators manage user accounts in the identity provider. Users' credentials continue to be authenticated by the identity provider and not Nintex CE Platform. Any password policies that are established for your organization such as password length or password change every month, are also in effect for Nintex CE Platform.
-
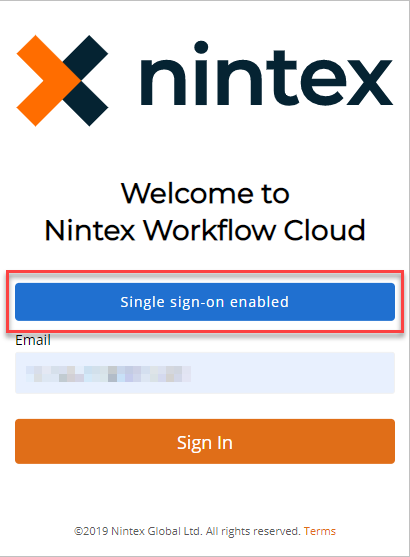
Auto-onboarding: Users within the domain will be automatically onboarded when they access Nintex CE Platform, allowing just-in-time provisioning of users. Auto-onboarding is subject to rate limiting and should not be used for bulk onboarding.
Do I need to bulk onboard users when single sign-on is configured?
When users access a form, task, workflow, or My Nintex, they are automatically onboarded. This eliminates the need for a bulk onboarding process when federating Nintex CE Platform with your Identity Provider. For more information on enabling authenticated task assignments, see Enable Assignee authentication.
What do I need to configure SAML for Nintex CE Platform using my preferred identity provider?
Before configuring SAML in Nintex CE Platform, make sure you have:
- An email address with an administrator role in the Nintex CE Platform tenant that you're going to configure with SAML. For example, admin@YourDomain.com.
- An email address with an administrator role in the identity provider.
Enabling single sign-on in your tenant will also enable single sign-on in associated Nintex CE Platform tenants. For example, both sales-myorg.workflowcloud.com and hr-myorg.workflowcloud.com will be enabled with single sign-on if you configure SAML in either of them.
How do I configure SAML in my Nintex CE Platform tenant?
To configure identity provider for Nintex CE Platform using SAML protocol, see the guide listed below that is relevant to the Identity provider you use:
- Configure SAML with Okta as identity provider
- Configure SAML with OneLogin as identity provider
- Configure SAML with PingOne as identity provider
- Configure SAML with Google Suite as identity provider
- Configure SAML with Active Directory Federation Services as identity provider
- Configure SAML with other identity providers (a generic guide) (a guide to be used for identity providers not listed above)
Which identity claims does Nintex CE Platform require from the identity provider?
The following attributes are requested from the identity provider:
- First name
- Last name
Security-related questions about SAML configuration in Nintex CE Platform
Aside from SAML, what other federation protocols does Nintex CE Platform support?
Currently, Nintex CE Platform supports the following:
- Service provider-initiated SAML
- OpenID Connect An authentication protocol based on the OAuth 2.0 family of specifications. (OIDC) via Active Directory
Are there specific conditions required to access Nintex CE Platform?
Nintex is a software as service that doesn’t need any special access conditions. Only username and password are required to sign in.
Does Nintex CE Platform have its own ID store?
Nintex CE Platform does not store passwords. We have user mapping tables to the identity.
Will Nintex CE Platform transform identity data such as an e-mail address?
No transformation required.
Can Nintex CE Platform prevent access to unauthorized users?
Once users are authenticated with the identity provider, users are authorized based on their roles in NWC. For more information on roles, see User roles.
Can Nintex CE Platform sign SAML requests?
No. Signing SAML requests is not currently supported.
Does Nintex CE Platform have a token encryption certificate?
We do not support token encryption certificates.
Which type of certificates does Nintex CE Platform use? What is the lifetime of each certificate?
Nintex CE Platform only uses the certificates provided from the identity providers. The lifetime of each certificate is dependent on the providers.
Is there a process in place to replace certificates before those certificates expire?
Yes. An administrator can replace certificates in the User Management page of Nintex CE Platform.
Does Nintex CE Platform support and configure two token signing certificates for the trusted federation system?
No.
Does Nintex CE Platform support Single Log Out (SLO)?
SLO is not supported. We only support SP-initiated SSO.
What is the authorization model for Nintex CE Platform?
Roles are managed in Nintex CE Platform. For more information on user roles, see User roles.
Does Nintex CE Platform need any authorization data from the identity provider?
No. Nintex CE Platform only requires email, firstname and lastname.
Troubleshooting
 The mapping for your IdP SAML attributes is incorrect - Attribute are missing
Issue
This error may occur after configuring Azure Active Directory identity federation in Nintex CE Platform.
Cause
This error happens because Nintex CE Platform requires the first name, last name, and email attributes to be provided by the Identity Provider (IdP) for the user to successfully access Nintex CE Platform.
Resolution
If any of the attributes are missing, there are two ways to resolve the issue:
-
The IdP administrator can manually add the missing attribute for all the affected users in their IdP.
-
The IdP administrator can apply rules in SAML mapping to pick a default attribute for the missing attribute.
Add the rule:
-
Go to the Enterprise application where SSO is configured.
-
Under Manage, click on Single sign on.
-
Edit Attributes & Claims.
-
Click on the claim name of the attribute that is missing.
-
Define the following fields:
-
Source: Transformation
-
Transformation: IfEmpty()
-
Parameter 1 (input): Attribute
-
Attribute name: user.surname
-
Parameter 2 (output): Attribute
-
Attribute name: user.givenname
-
-
Click Add.
-
Click Save.
Unable to sign in to Nintex Workflow dashboard after SSO upgrade
Issue
Users are unable to sign in to the Nintex Workflow dashboard and encounters a forbidden error with code 305.
Cause
The mapping of your IdP SAML email address attribute is incorrect. Check your IdP configuration. Try signing out and signing in again. If the problem continues, contact your Nintex Workflow administrator to arrange access.
Resolution
-
Go to Entra SAML Single Sign-On for Nintex Workflow.
-
Click Edit under Attributes and Claims.
-
Click on each entry of the Additional Claims and verify the value as per the following:
Name Namespace emailaddress
http://schemas.xmlsoap.org/ws/2005/05/identity/claims/emailaddress
givenname
http://schemas.xmlsoap.org/ws/2005/05/identity/claims/givenname
name
http://schemas.xmlsoap.org/ws/2005/05/identity/claims/name
surname http://schemas.xmlsoap.org/ws/2005/05/identity/claims/surname
Note: Ensure that the namespace value for all four attributes is set to: http://schemas.xmlsoap.org/ws/2005/05/identity/claims